From first conversation to audit-ready
SimpleAudit uses AI to do the compliance work. You review and approve. Here's how it works in 5 steps.
Read the transcript
Every founder knows this moment. Getting SOC 2 ready can take months to figure out, and the cost of getting help makes it even harder. Most founders don't know where to begin. SimpleAudit starts with a conversation, plain language, no jargon. From one conversation, your entire workspace is built, personalized to your stack, built for founders, clear next steps every time. Policies are drafted automatically, based on your answers. Refine any policy with AI suggestions that highlight what matters. Every module comes with built-in guidance. Vendors, risks, access reviews, handled with AI that knows your setup. Your SOC 2 readiness updates in real time. Clear progress, no guesswork. Review security assessments, store evidence, and stay organized, all in one place. Complete your business impact analysis with guided step-by-step prompts. Most startups spend up to $20,000 on software and consultants just to get ready. SimpleAudit starts at $199 a month. Right-sized SOC 2 for startups. You're closer than you think. Start your free trial. No credit card. No setup. SimpleAudit.io.
Get ready
Discovery conversation
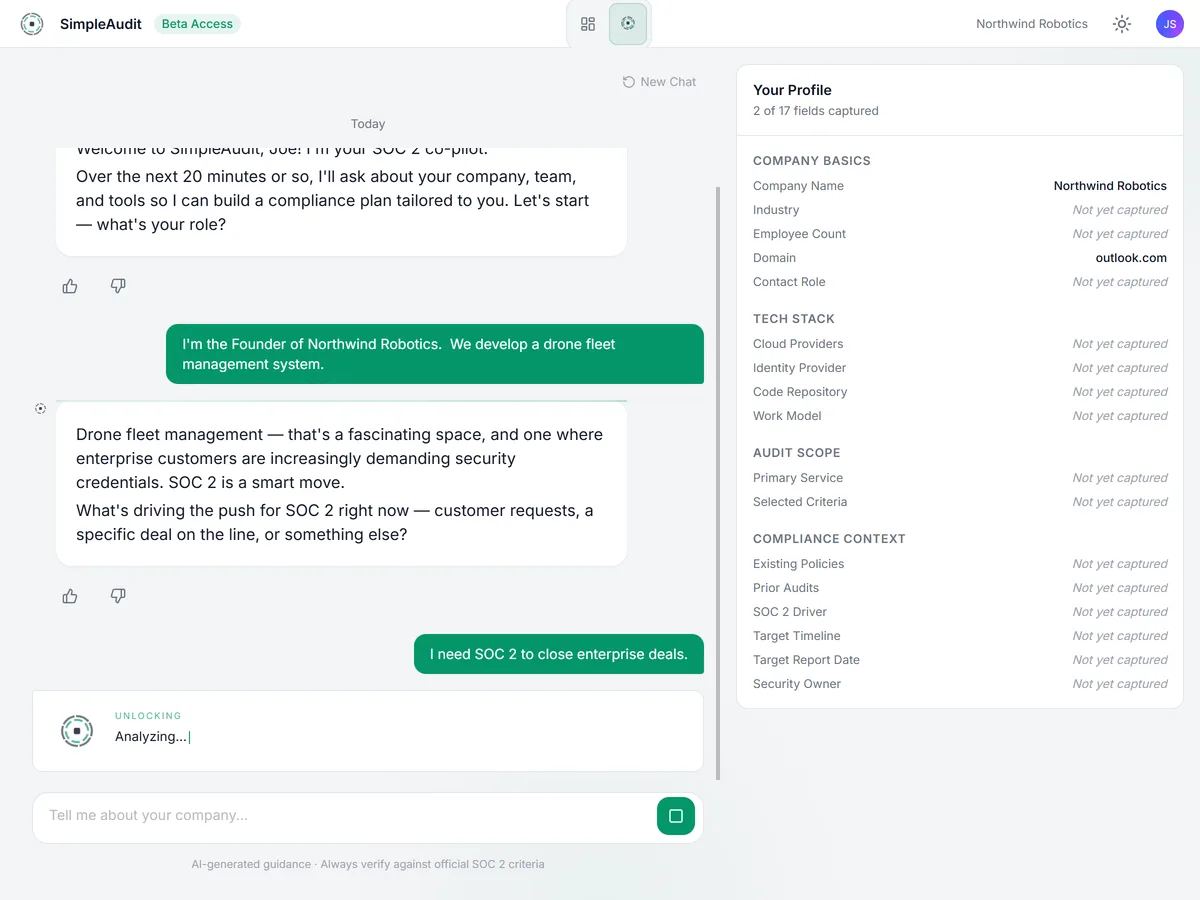
Tell us about your company
The AI asks plain-English questions about your company: cloud providers, team size, tools you use, data types you handle, and your existing security practices. No forms, no jargon. Just a conversation.
- Takes about 15-20 minutes
- Covers infrastructure, team, data handling, and existing security
- AI learns your context so everything it generates is customized
Business Impact Analysis
Identify what matters most
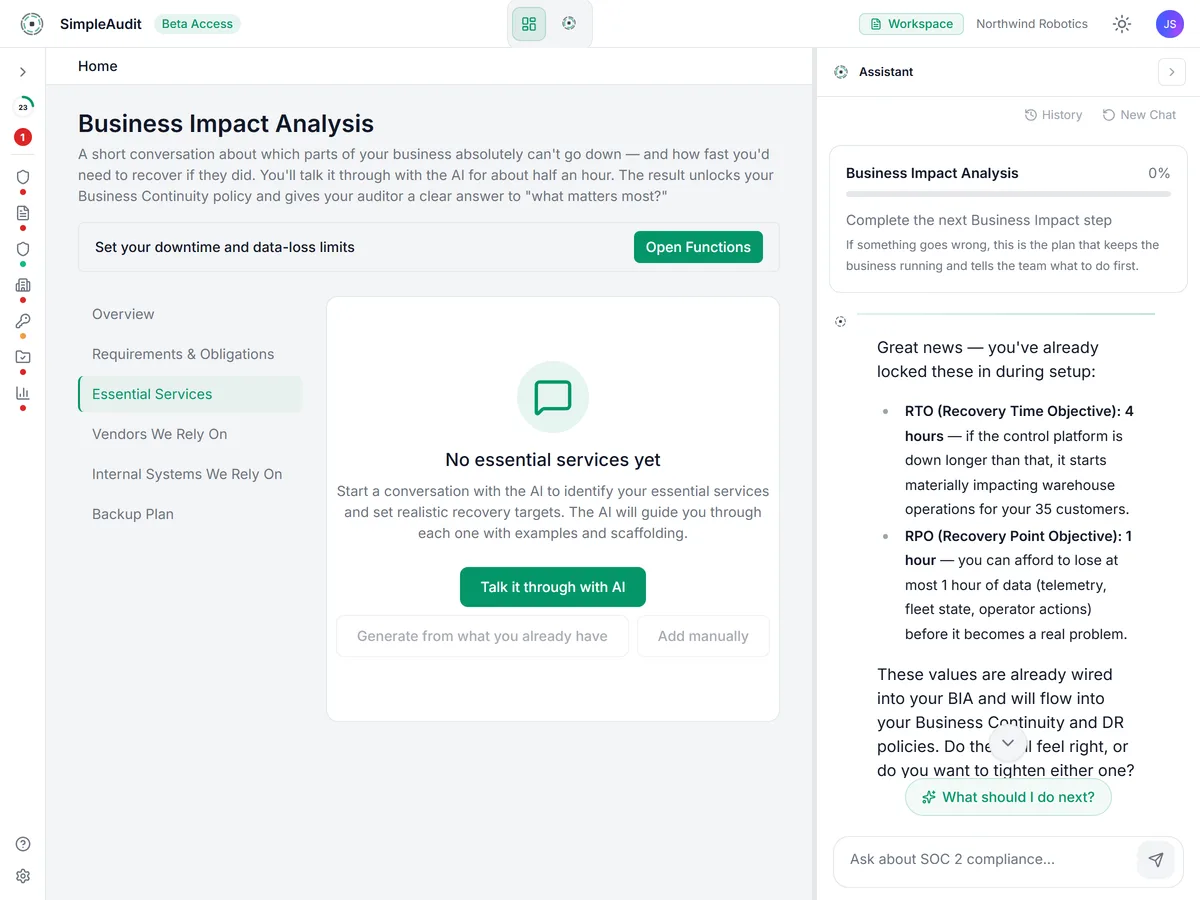
AI-led conversational identification of business functions, criticality tiers, RTO/RPO, dependencies, and recovery teams. Generates BC and DR plans grounded in real recovery objectives.
- Conversational Functions tab: AI helps you identify business functions and criticality tiers
- Capture RTO/RPO, dependencies, and recovery teams across 6 BIA tabs
- Generate BC and DR plans grounded in your real recovery objectives
Policy generation
Review AI-generated policies
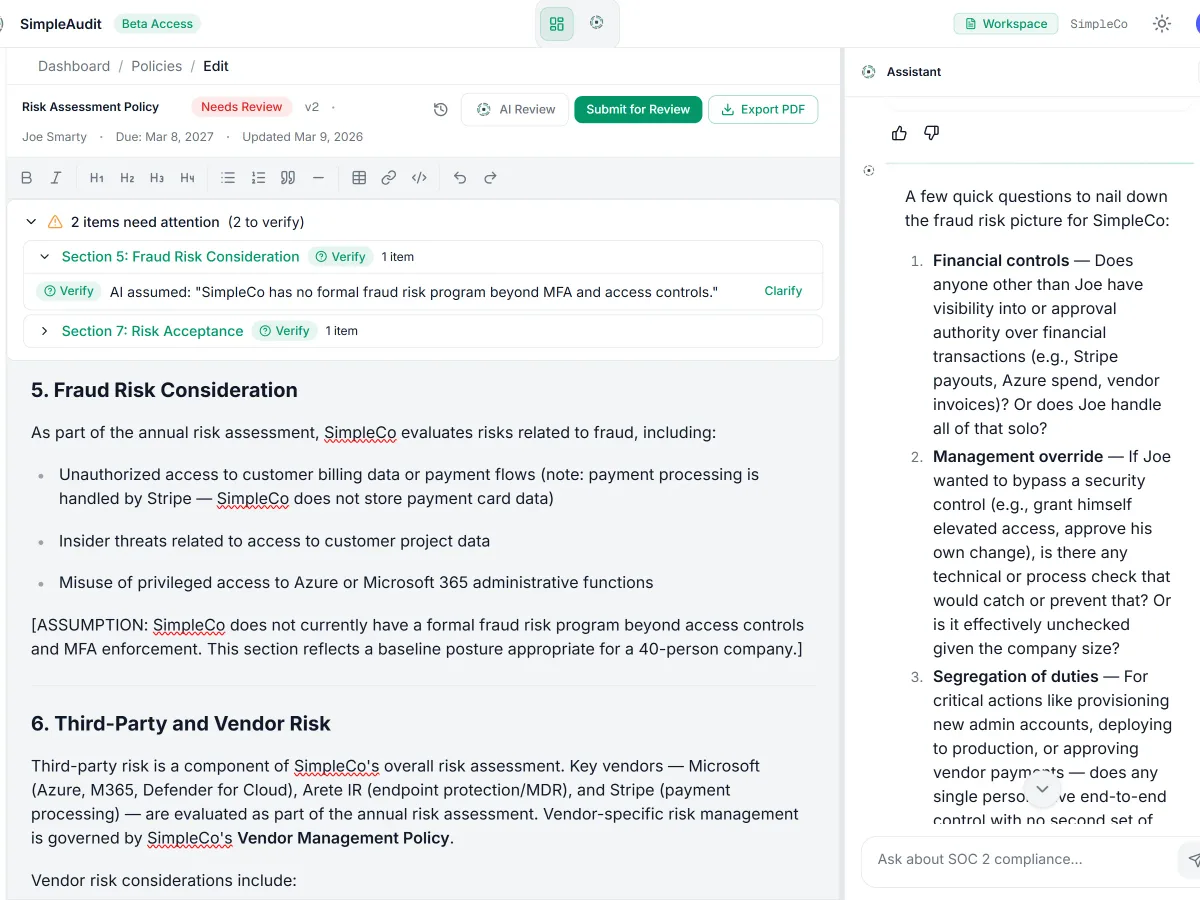
Based on your answers, the AI generates SOC 2 policies customized to your actual business. Not templates: policies that reflect your tools, your team structure, and how you operate.
- Policies match your specific tech stack and processes
- Rich text editor for review and refinement
- Version history tracks every change
- Approval workflows for team review
Evidence + remediation
Close the gaps
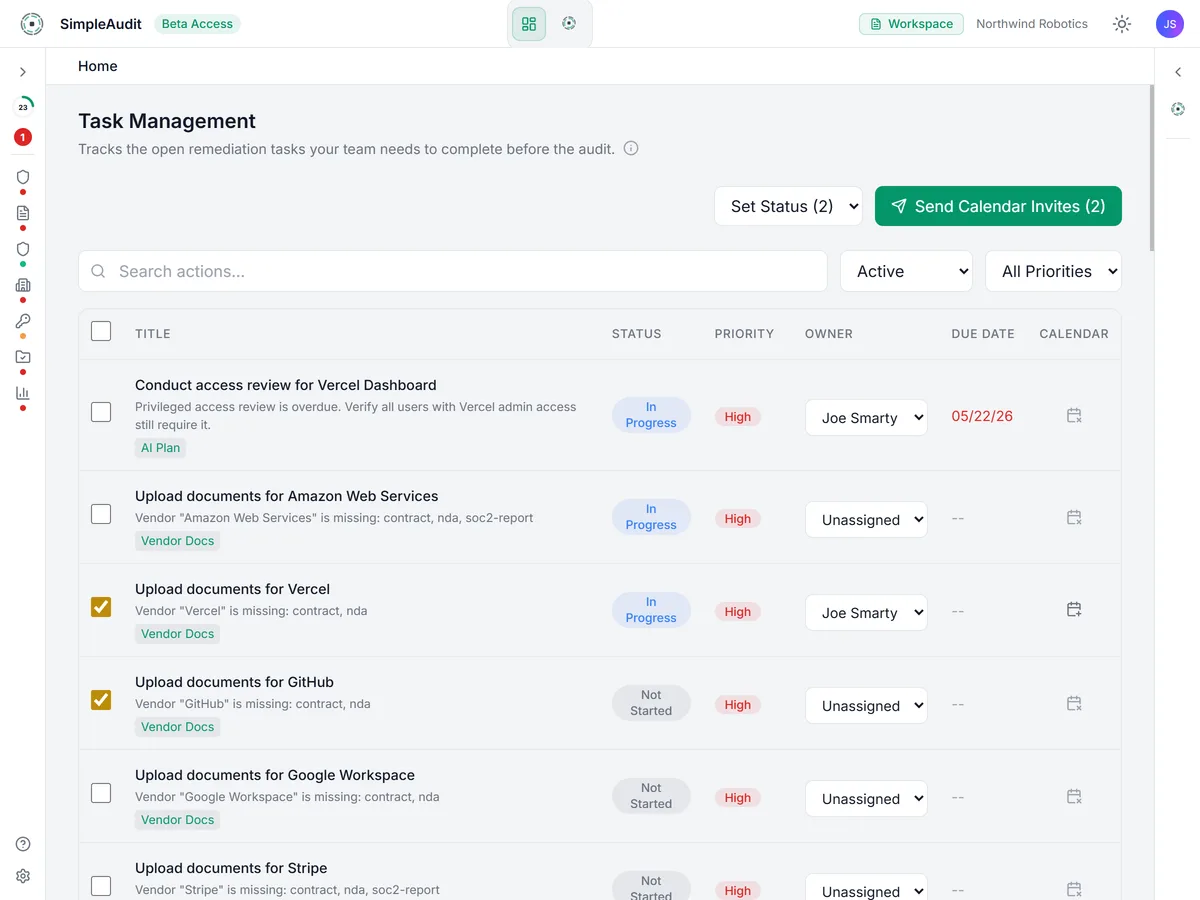
AI generates a prioritized task plan and tells you what evidence to collect by control area. Upload it yourself, or on Prove, let an AI agent push it straight to your vault, and everything is cross-linked so nothing falls through the cracks.
- AI-generated task plans from compliance gaps
- Evidence collection guidance by control area
- Push evidence via the MCP connector or API (Prove), or upload it yourself
- Cross-linked tasks, evidence, and controls
- Calendar integration for scheduled reviews
Audit readiness
Know when you're ready
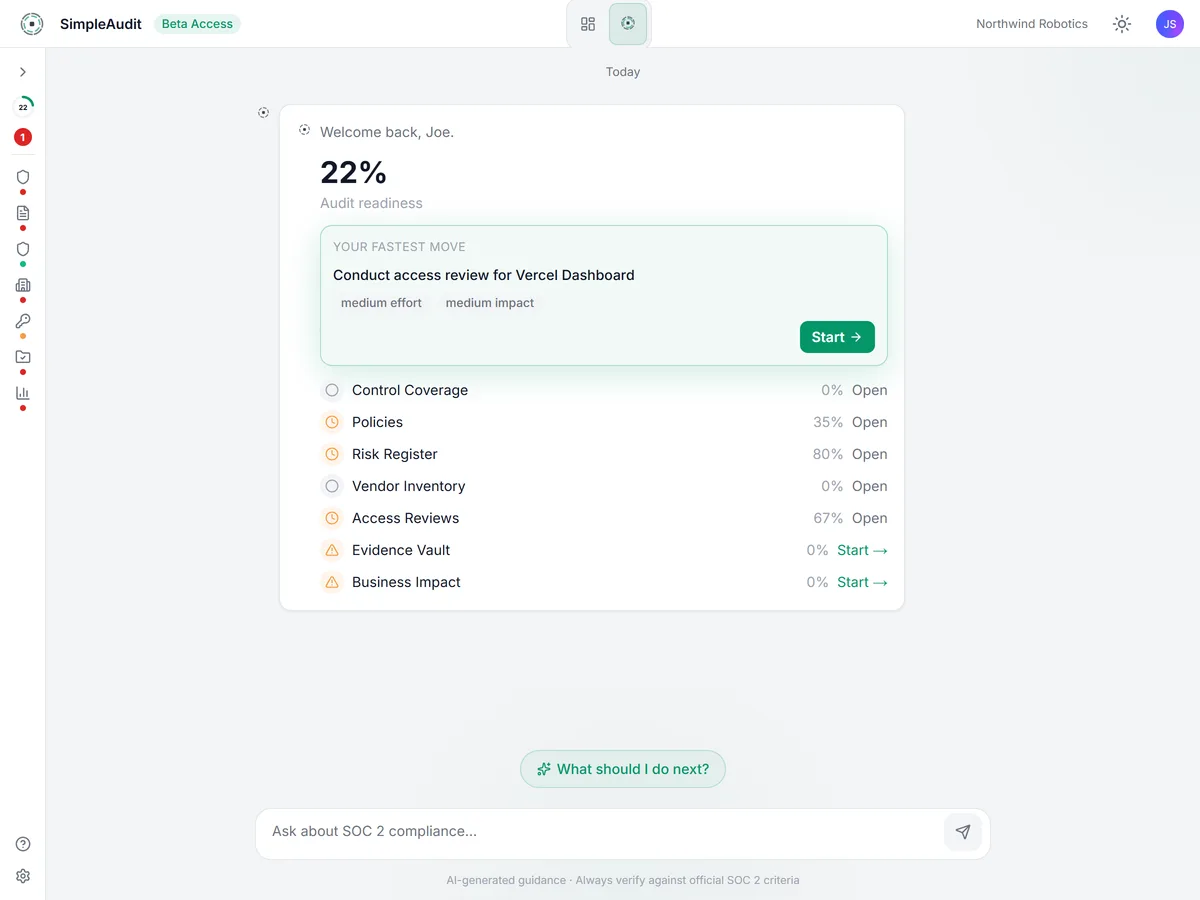
Real-time readiness scoring across 6 compliance areas: policies, risks, vendors, evidence, access reviews, and tasks. Watch your scores climb as you complete work. When you hit your targets, you're ready for your auditor.
- Six-area dashboard with real-time progress
- AI recommendations with urgency and effort scoring
- Audit period tracking with countdown
- Export evidence packages for your auditor
Win deals and pass audits
These moments do not wait for your report. Use each tool the day it comes up.
When a buyer asks
“A prospect just sent you a security questionnaire”
Security Questionnaires
Prove and SellEach answer comes from your own policies and records, marked by where it came from.
Read the transcript
The deal is waiting on a spreadsheet. A prospect sends a SIG Lite, and the deal waits until it comes back. Someone copies last year's answers and promises a few things you don't actually do. Your auditor finds the mismatch later. Each answer cites your policy or your records. Questions SimpleAudit can't back become plain questions for you, and any new promise puts a policy update on your to-do list. The questionnaire goes back in days, your answers match what your auditor sees, and saved answers make the next one faster.
“Their legal team attached Exhibit C”
Contract Review
Prove and SellEach security clause is marked Covered, Partly covered or Not covered against your policies, with a fix for every gap.
Read the transcript
Exhibit C. Your customer's security exhibit says you will report a breach within 24 hours. Your policy says 72. Legal reads the liability clause and sales reads the price. Nobody reads Exhibit C, and you sign a promise you don't keep. SimpleAudit marks every security clause Covered, Partly covered or Not covered, and quotes your policy where it is covered. Each gap says how to fix it: update your policy when the ask is normal, or push back with replacement wording when it goes beyond SOC 2 norms for a company your size. On a supplier's contract, it asks for stronger terms and never lowers your bar. You sign knowing every security promise in the contract is one you already keep.
When your auditor asks
“Show me your policy is actually followed”
Policy vs. Reality
ProveAI checks your policies against your real evidence and flags where they disagree before your auditor does.
Read the transcript
The policy says quarterly. Your access policy says you review who has access every quarter. Your records show one review, last year. Nobody compares the two until your auditor does. The missed reviews become a finding in your SOC 2 report. Policy vs. Reality checks what your policies promise against your evidence and flags the gap when the two stop matching. It opens a task to close it, and you decide whether to run the missing reviews or update the policy. You close the gap before your audit starts, and your auditor sees a policy and records that agree.
“When did you last test your incident plan?”
AI Tabletop Exercises
ProveAI writes an incident response, continuity or disaster recovery exercise from your own systems, and the after-action report is saved as evidence.
Read the transcript
The plan nobody has tested. Your auditor asks when you last tested your incident response plan. The plan exists, but nobody has ever run it. You hire a consultant for a day, or you skip the test and hope the question does not come up again. SimpleAudit writes an incident exercise around your own systems and vendors, and your team works through it on your usual video call. You record each decision as the ransom note and the news headline appear on screen. You sign off the after-action report, it is saved as evidence, and your answer to the auditor is a date and a document.
A public security page where buyers request documents and you approve each one. See Trust Center →
We never touch your infrastructure
Evidence arrives only when you or your AI agent sends it, which turns out to be both simpler and safer than connecting your systems.
One connector, not fifty
Pull-based tools ask you to wire up your cloud, identity, and dev systems one integration at a time: IAM roles, OAuth grants, an endpoint agent on every laptop. SimpleAudit is one step: add the connector, authorize once (write-only), done.
One-line push for agent-using teams
If your team already uses an AI agent like Claude Code or Cursor, pushing evidence is a one-line instruction: "upload our Q3 access review and tag it access-controls", with no new tool to learn. Prefer to do it by hand? Upload works exactly as before.
Nothing to break, nothing to steal
A push connector has no standing connection to your systems: nothing to silently disconnect when a token expires, and nothing an attacker could steal to reach your infrastructure. When credential-holding vendors were breached: Sisense (a CISA-ordered mass credential reset in 2024), Okta (pivoted into Cloudflare and 1Password), CircleCI ("rotate every secret"). Their customers paid. A breach of SimpleAudit yields none of that access.
Ready to start the conversation?
Start your free trial. The AI handles compliance. You handle your business.
Start Free Trial