Everything you need for SOC 2
Eight integrated modules. One workspace. Zero integrations required.
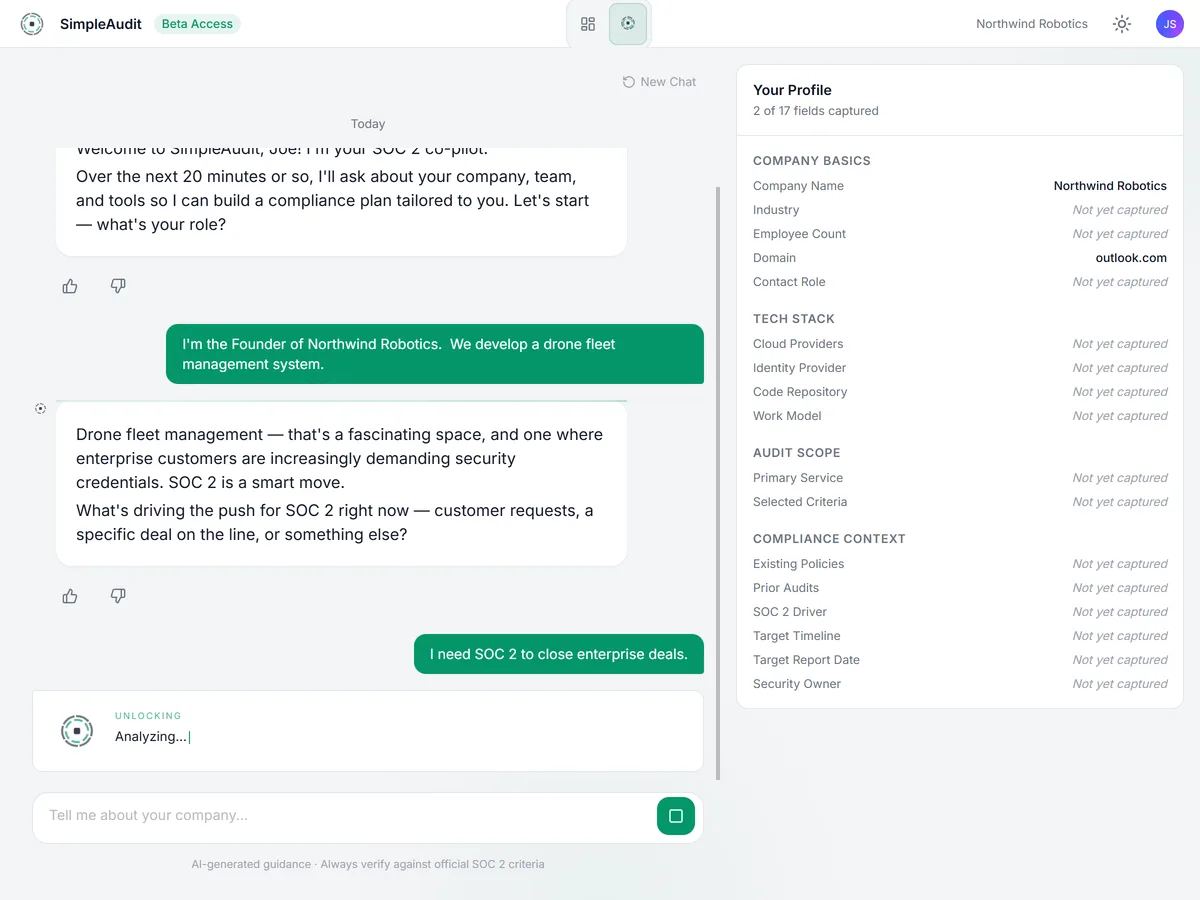
AI Policy Builder
Chat. Review. Approve. SOC 2 policies generated from a conversation with version history and approval workflows.
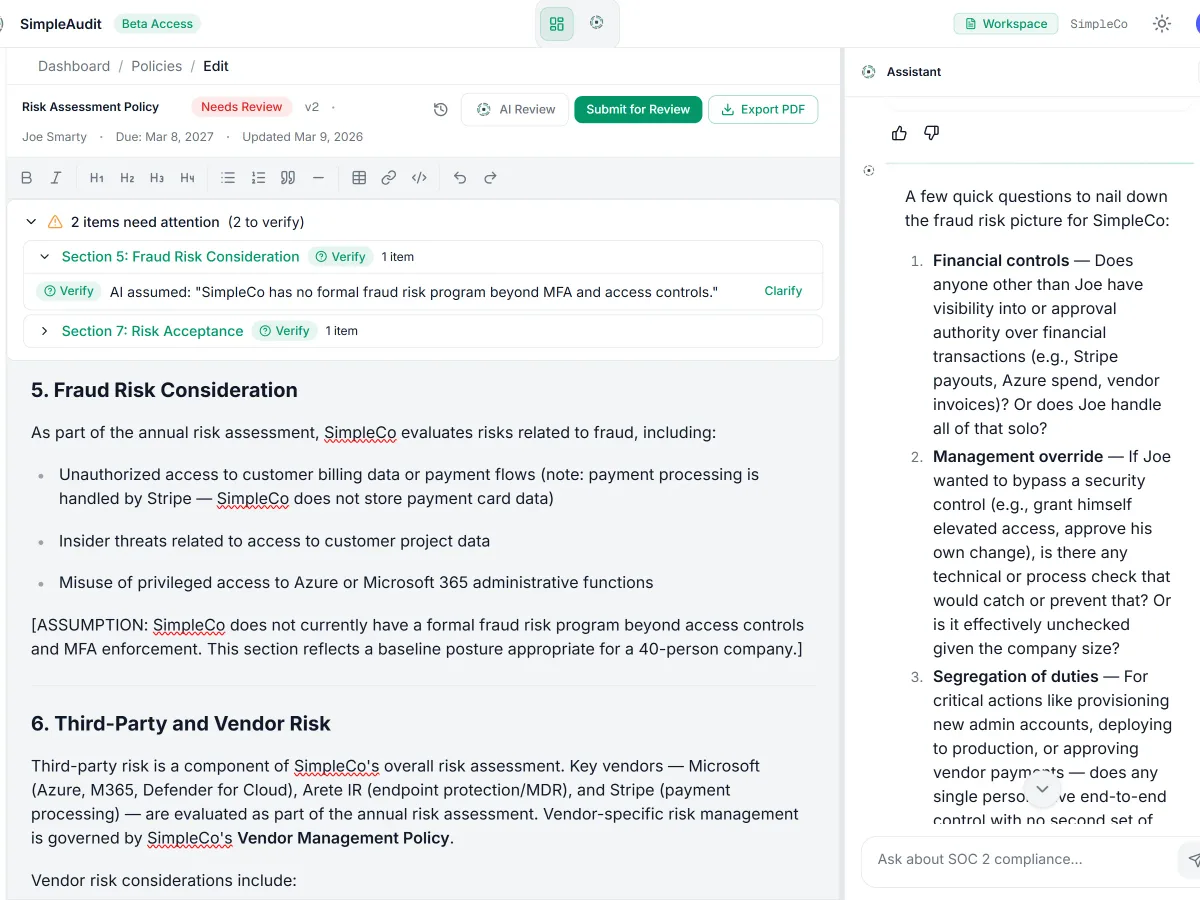
Risk Register
AI-suggested risks, rated before and after controls, with your decision, sign-off and an auditor workbook.
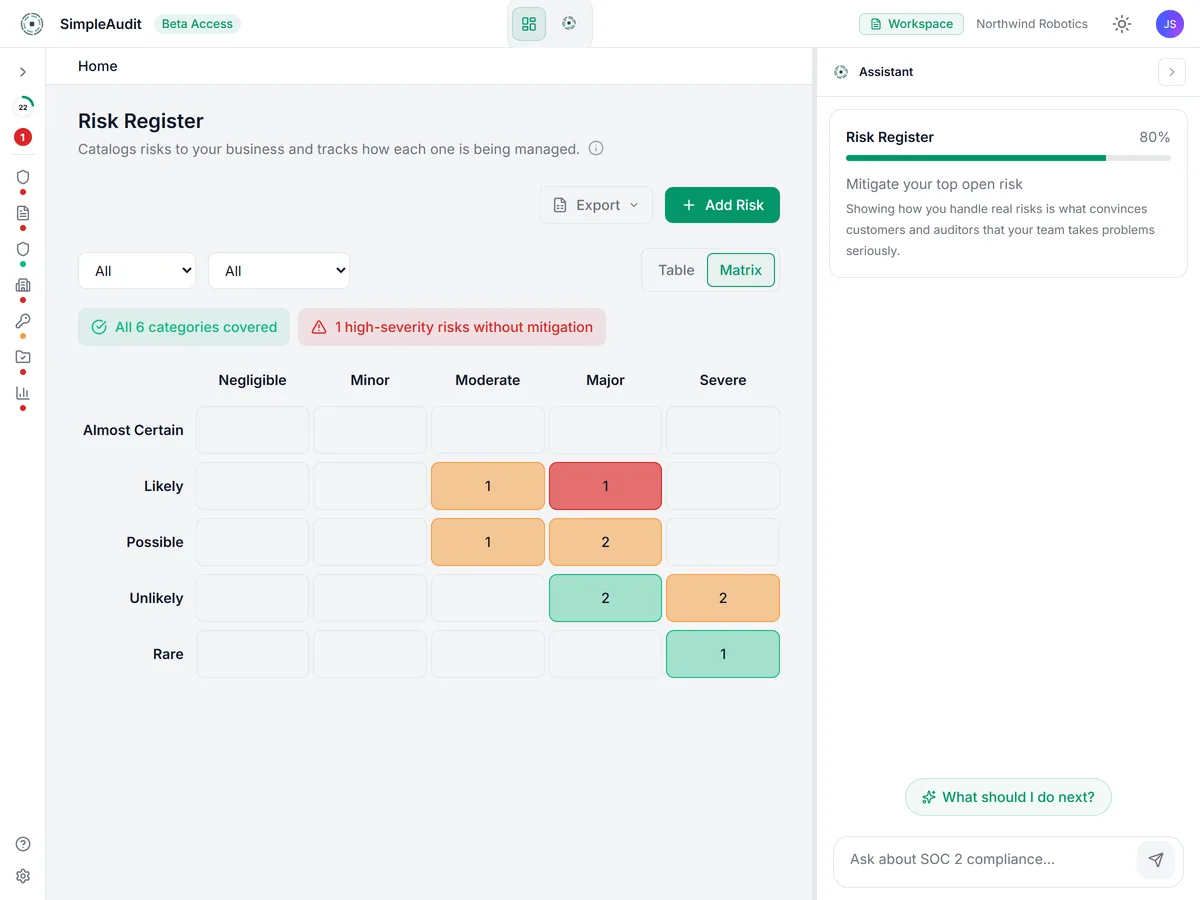
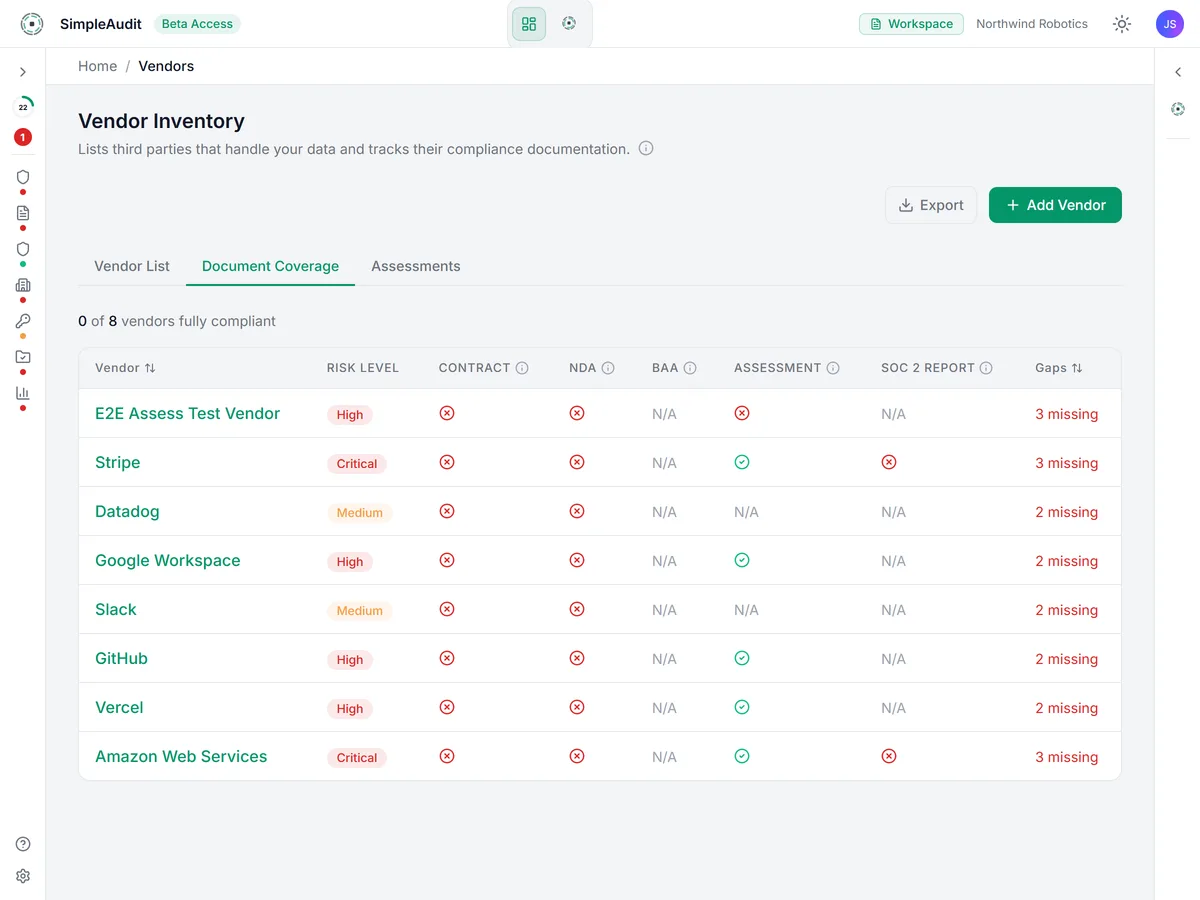
Vendor Management
AI identifies your vendors. Document gap alerts. Security questionnaires and risk-level tracking.
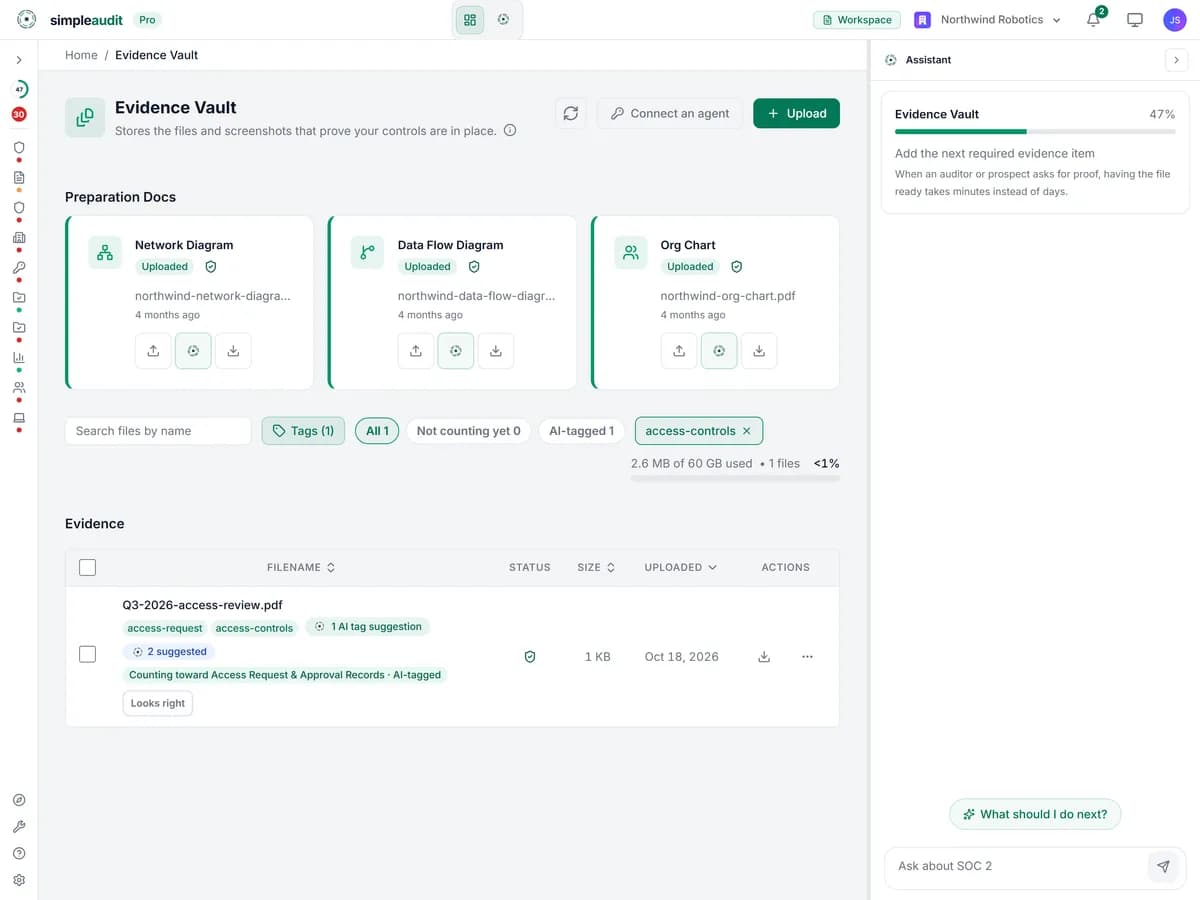
Evidence Vault
Version-controlled storage with full audit trail. Organized by control area. One-click export.
Access Reviews
Application registry with review scheduling. Calendar invites. AI identifies your apps.
Task Management
AI-generated task plans. Smart suggestions. Cross-feature integration with policies, risks, and reviews.
Journey Readiness
Six-step progress tracker. Know exactly when you're audit-ready across policies, risks, vendors, and more.
Connect Your AI Agents
Your AI agents push evidence straight into the vault via the MCP connector or API, and AI three-way reconciliation keeps it honest. Prove plan.
When a buyer or auditor asks
Buyers and auditors do not wait for your report. Each tool answers one of their questions.
Trust Center
Prove and SellA public security page built from your SOC 2 work. Buyers request documents and you approve each one before anything is shared.
Explore Trust CenterWhen a buyer asks
Security Questionnaires
Prove and SellUpload a questionnaire from a customer. Each answer is taken from your records, quoted from your policy, or marked for you to fill.
Explore Security QuestionnairesWhen a buyer asks
Contract Review
Prove and SellUpload a customer or supplier contract. Each security clause is marked Covered, Partly covered or Not covered against your policies, with a suggested fix for every gap.
Explore Contract ReviewWhen your auditor asks
Policy vs. Reality
ProveEvery night, AI compares what your policies promise with your evidence and your SOC 2 controls, then flags where they disagree. Each gap becomes a task, and you decide how to close it.
Explore Policy vs. RealityWhen your auditor asks
AI Tabletop Exercises
ProveAI writes an incident response, continuity or disaster recovery exercise from your own systems. Run it with your team or on your own, and the signed-off report is saved as evidence.
Explore AI Tabletop ExercisesAI Policy Builder
Generate your SOC 2 policies through a guided AI conversation. The AI asks about your company, tools, and processes, then drafts policies customized to your business. Edit in a rich text editor, track versions, and manage approval workflows.
Risk Register
Identify risks with AI suggestions based on your company profile, rate each one before and after your controls (inherent and residual risk), record what you decided to do about it, and get the sign-off an auditor looks for. Built after a CPA SOC 2 auditor reviewed the register and asked for standard risk-assessment terms, so one export is set up to answer the risk assessment criteria (CC3.1 to CC3.4) and the risk mitigation criterion (CC9.1) without a conversation.
Vendor Management
The AI identifies your vendors from your company profile. Track vendor risk levels, send and manage security questionnaires, get alerts when vendor documentation is missing or expired, and maintain a complete vendor inventory for your auditor.
Evidence Vault
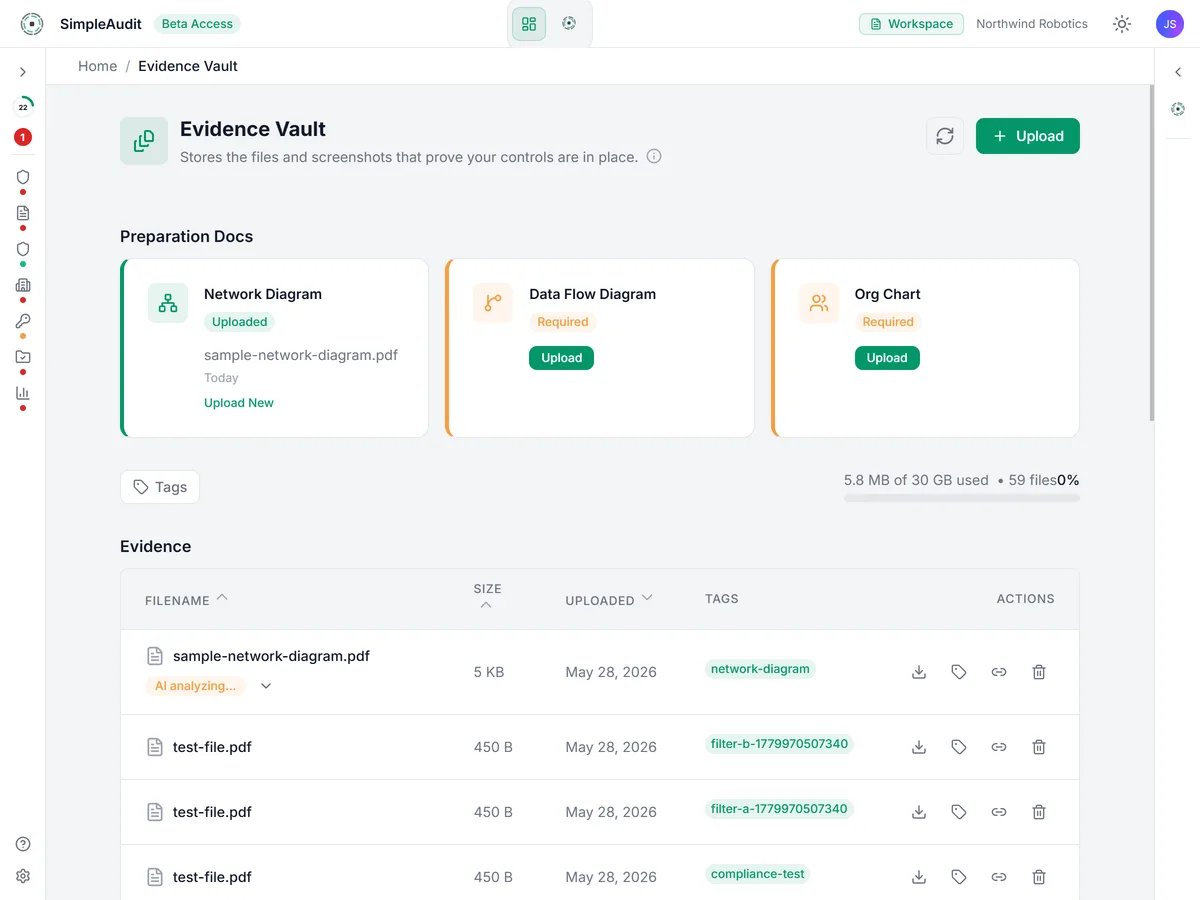
Upload and organize compliance evidence in a version-controlled vault. Every file has a full audit trail showing who uploaded it and when. Organized by SOC 2 control area with tagging, search, and one-click export for auditor deliverables. Evidence gets in two ways: upload it yourself, or on Prove, let an AI agent push it straight in via the MCP connector or API. SimpleAudit never connects to your systems.
Access Reviews
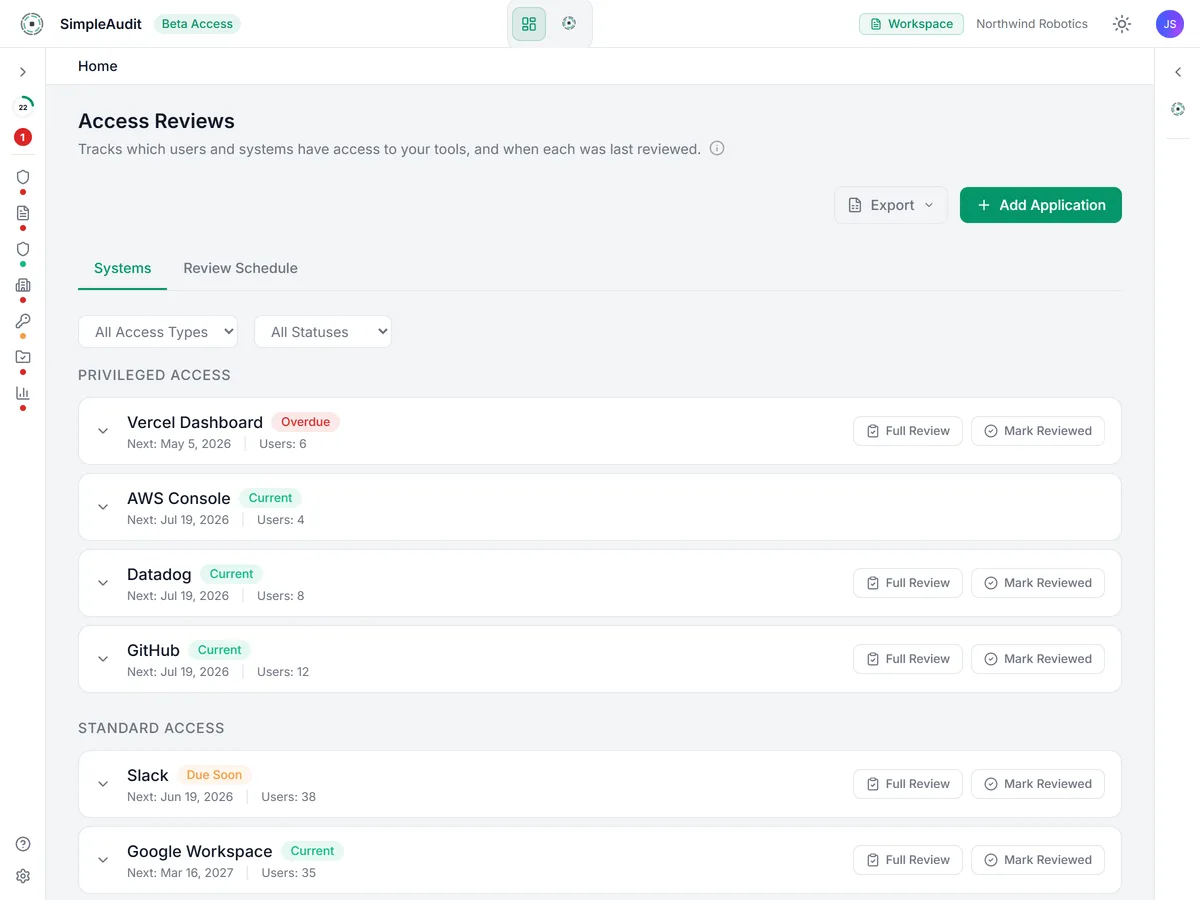
Maintain an application registry with scheduled access reviews. The AI identifies applications from your company profile. Schedule recurring reviews, send calendar invites to reviewers, and document access decisions with an audit trail.
Task Management
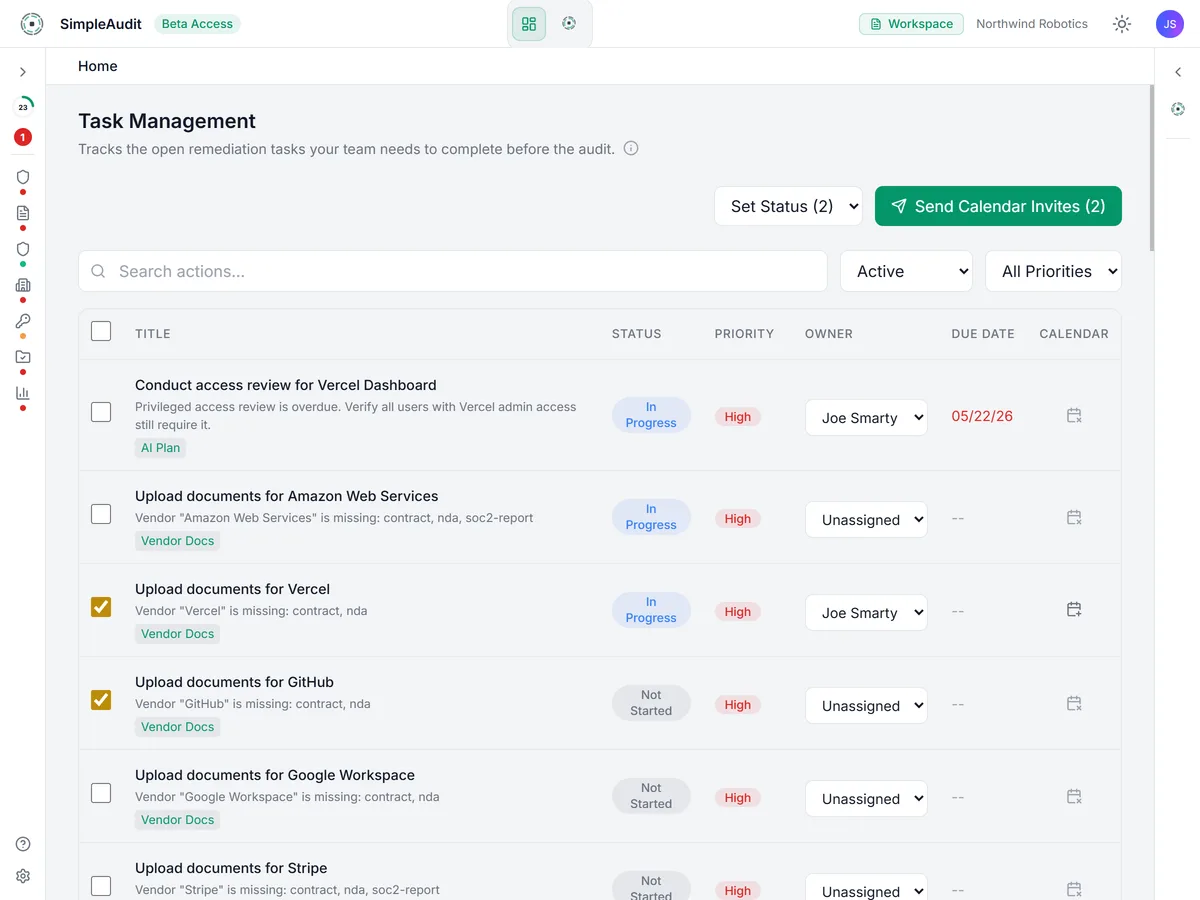
Get AI-generated task plans based on your compliance gaps. Use AI-suggested tasks for common SOC 2 activities. Tasks integrate across policies, risks, vendors, and access reviews so nothing falls through the cracks.
Journey Readiness
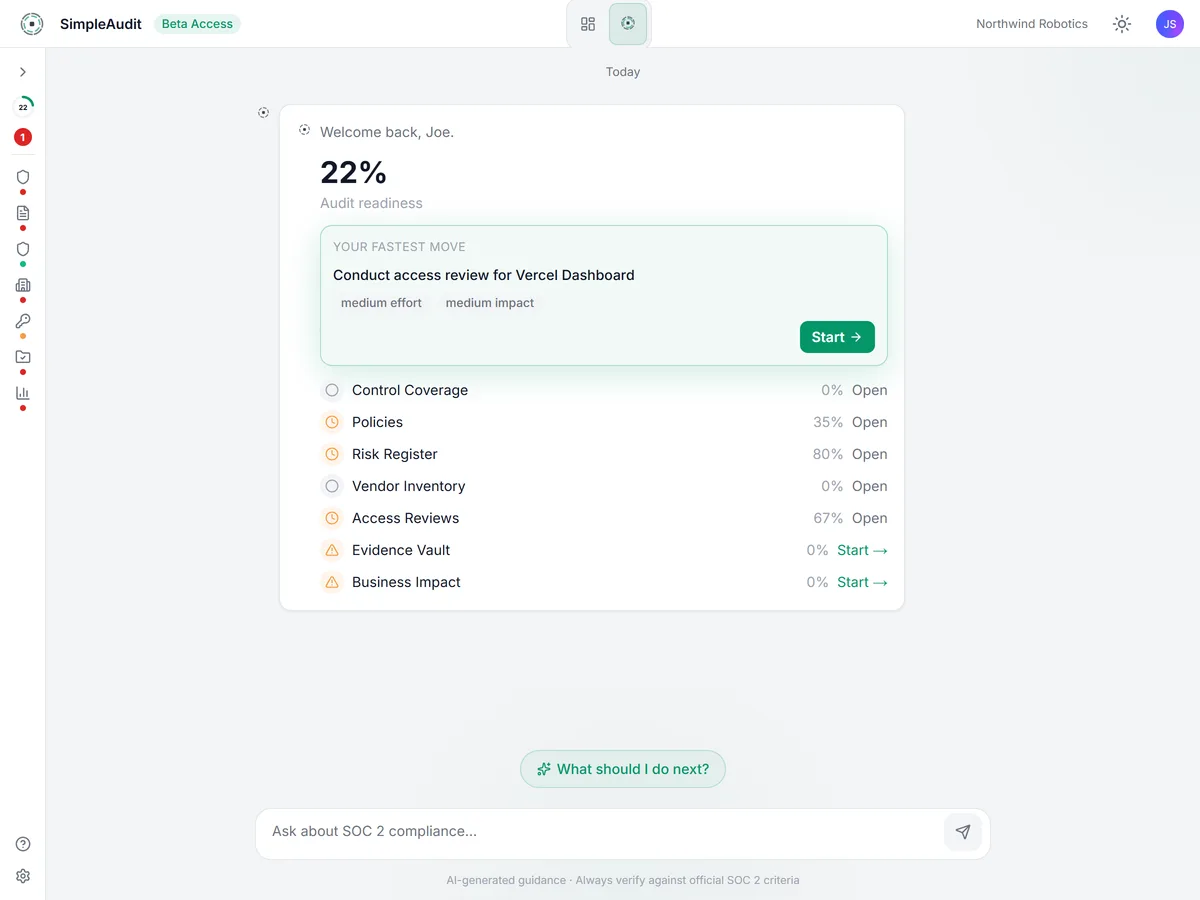
Track your SOC 2 readiness across six compliance areas: policies, risks, vendors, evidence, access reviews, and tasks. See real-time progress percentages and know exactly what remains before you're audit-ready.
Connect Your AI Agents
On the Prove plan, SOC 2 evidence collection becomes something your AI agents do for you. Connect any agent (Claude, ChatGPT, or your own) through SimpleAudit's MCP connector, or push from scripts and CI pipelines via the REST API. It's agentless in the other direction: SimpleAudit never connects to your infrastructure, so there are no integrations to wire up and no access to grant. Every pushed file lands version-controlled, auto-tagged, and mapped to the right SOC 2 controls, and AI three-way reconciliation continuously checks your policies, your evidence, and the SOC 2 standard against each other, turning drift into tasks before it becomes an audit finding.
Ready to get started?
Start your free trial and experience AI-native SOC 2 compliance.
Start Free Trial